HeroPerks

Data Processing Roles

Understanding how personal data flows through the platform requires clarity about the roles held by each party involved. This page sets out those roles and responsibilities.

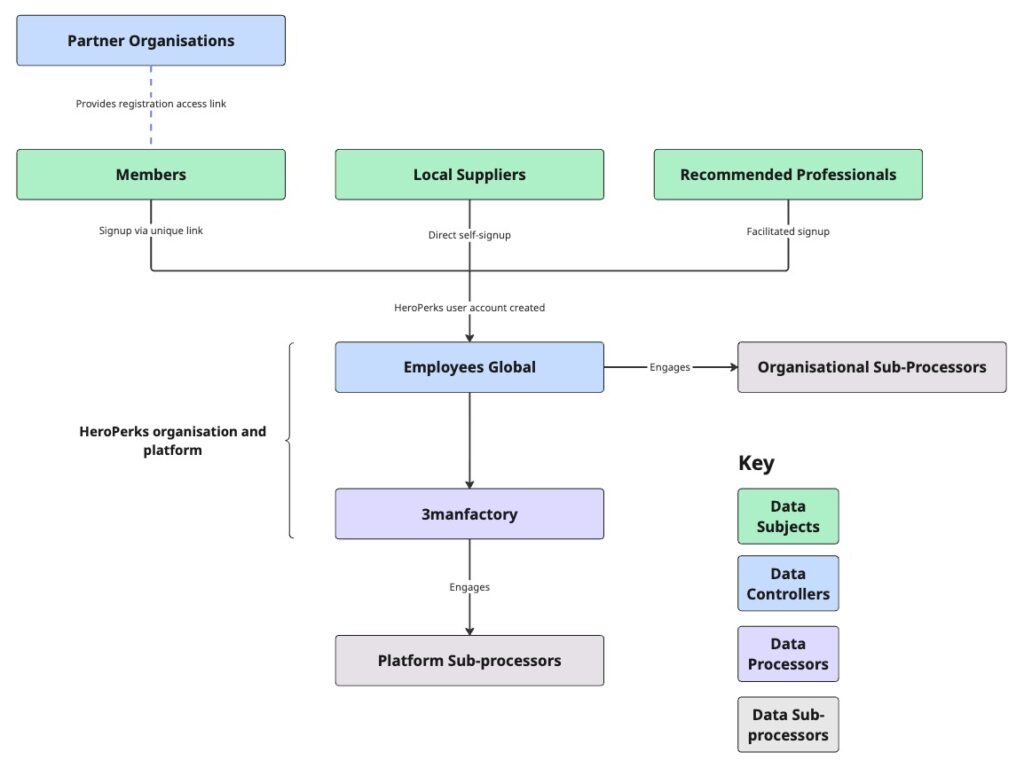
Data Controller Employees Global Ltd (trading as HeroPerks) acts as the Data Controller for personal data processed through the platform. As Controller, Employees Global Ltd determines the purpose and means of processing personal data and holds primary responsibility for compliance with UK GDPR.

Data Processor 3manfactory Ltd acts as Data Processor on behalf of Employees Global Ltd. 3manfactory processes personal data solely as required to provide hosting, maintenance, and technical operation of the platform, strictly in accordance with Employees Global Ltd’s instructions.

Sub-Processors 3manfactory engages a small number of third-party sub-processors to deliver platform services. These are listed on the Platform Sub-Processors page.

Partner Organisations Partner Organisations act as Data Controllers in their own right in respect of their employees’ data. When a Partner Organisation shares employee data with the platform to enable Member registration, they do so under their own lawful basis and in accordance with their agreement with Employees Global Ltd.

The Processing Chain

Personal data collected directly from Members, Local Suppliers, and Recommended Professionals at registration and during platform use is processed by Employees Global Ltd as Controller, with 3manfactory acting as Processor for the technical operation of the platform.


Legal responsibility for the content on this page sits with Employees Global Ltd.
Platform Data Handling

Personal data processed through the platform is limited to what is strictly necessary for the operation of the service.

Data Collected at Registration The following personal data is collected when a user creates an account:

  • Name
  • Email address

No special category data is collected or processed through the platform.

Data Processed During Platform Use Additional data is generated and processed as a result of platform activity, including:

  • Platform usage and activity data
  • Profile information
  • Offer redemption activity

This data is used to operate the platform and deliver personalised and triggered communications. See Platform Sub-Processors for details of third parties involved in processing this data.

Data Storage Personal data is stored in two locations:

  • The platform database, hosted on managed private server infrastructure in the United Kingdom
  • Brevo, used for email delivery and marketing automation, hosted in the European Union

Data Transfers No personal data is transferred outside the United Kingdom or European Union.

Access to Data Access to personal data held within the platform is limited to authorised personnel only. Personal data is accessed only as required to deliver platform services, and not for any independent purpose.


Legal responsibility for the content on this page sits with 3manfactory Ltd.

Data Handling Policy

HeroPerks is committed to handling personal data responsibly, transparently, and securely. This policy explains how we collect, use, store, and protect personal data in line with UK data protection laws, including the UK GDPR and the Data Protection Act 2018.

1. Purpose of This Policy

This policy ensures that all personal data handled by HeroPerks is:

  • Processed lawfully, fairly, and transparently
  • Collected for specific and legitimate purposes
  • Limited to what is necessary
  • Accurate and kept up to date
  • Stored securely
  • Handled in line with individuals’ rights

2. Types of Data We Handle

We may collect and process the following types of data:

Personal Identification Data — Name, email address, contact details

Account Data — Login details, preferences, usage activity

Business / Partner Data — Company names, contact details, service information

Financial Data — Invoices, payment records (where applicable)

Technical Data — IP address, browser type, device data, cookies

Communication Data — Emails, enquiries, support messages

We do not intentionally collect sensitive (special category) data unless required and lawful.

3. How We Collect Data

We collect data through:

  • Website registrations and account creation
  • Email subscriptions and marketing sign-ups
  • Direct contact (email, phone, forms)
  • Partner onboarding processes
  • Cookies and analytics tools

4. How We Use Data

We use personal data to:

  • Provide and manage our services
  • Manage user accounts
  • Communicate with users and partners
  • Deliver relevant offers and updates
  • Improve our website and user experience
  • Process payments
  • Comply with legal obligations

5. Lawful Basis for Processing

We rely on the following lawful bases:

Consent — for marketing and optional communications

Contract — to deliver our services

Legal obligation — where required by law

Legitimate interests — for business operations and improvements

6. Data Sharing

We may share data with trusted third parties where necessary, including:

  • Technology and hosting providers
  • Email and communication platforms
  • Payment processors
  • Professional advisers (legal/accounting)
  • Regulatory authorities where required

All third parties are required to handle data securely and only for agreed purposes.

We do not sell personal data.

7. Data Storage and Security

We use appropriate measures to protect data, including:

  • Secure cloud-based systems
  • Access controls and permissions
  • Encryption where appropriate
  • Regular security monitoring
  • Staff awareness and training

Only authorised individuals can access personal data.

8. International Data Transfers

If data is transferred outside the UK, we ensure appropriate safeguards are in place, such as:

  • UK-approved adequacy decisions
  • Standard contractual clauses
  • Approved certification frameworks

9. Data Retention

We only retain personal data for as long as necessary. For full details, please see our Data Retention Policy.

10. Your Rights

Under UK data protection law, you have the right to:

  • Access your personal data
  • Correct inaccurate data
  • Request deletion (where applicable)
  • Restrict or object to processing
  • Request transfer of your data
  • Withdraw consent at any time

11. Data Breaches

We have procedures in place to detect, investigate, and report data breaches. Where required, we will notify the Information Commissioner’s Office (ICO) and affected individuals.

12. Responsibility and Governance

Responsibility for data protection sits with:

  • Company Directors
  • Appointed Data Protection Lead

All staff and partners must follow this policy, handle data securely, and report any concerns immediately.

13. Policy Review

This policy is reviewed at least once per year, or when legal or operational changes require updates.

14. Contact Us

If you have any questions about this policy or your data, please contact: [email protected]


Legal responsibility for the content on this page sits with Employees Global Ltd.
Backup and Log Retention

Backups Platform data is backed up daily. Backups are retained for a period sufficient to support platform recovery in the event of data loss, after which they are deleted. Backup data is subject to the same access controls as live platform data.

Operational Logs Server-level logs generated in the course of platform operation are retained for a limited period for the purposes of security monitoring, incident investigation, and performance management. Logs are not used for any purpose beyond platform operation.

Deletion On expiry of the applicable retention period, backup and log data is securely deleted.


Legal responsibility for the content on this page sits with 3manfactory Ltd.

Data Retention Policy

1. Retention Principles

HeroPerks is committed to ensuring that personal data is not retained for longer than necessary for the purposes for which it was collected, in accordance with the UK GDPR principle of storage limitation.

We will:

  • Only retain personal data where there is a valid business, legal, or regulatory reason
  • Regularly review the data we hold
  • Securely delete or anonymise data when it is no longer required

Retention periods are determined based on the purpose of processing, legal and regulatory obligations, contractual requirements, and legitimate business interests.

2. Categories of Data & Retention Periods

Customer / User Data — Account information, contact details, preferences. Retained for the duration of the account plus up to 24 months after last activity, for service provision, customer support, and re-engagement.

Marketing Data — Email subscriptions, communication preferences. Retained until consent is withdrawn or 24 months of inactivity, on the basis of legitimate interest and consent-based marketing.

Partner / Business Data — Business listings, contact details, agreements. Retained for the duration of the partnership plus 6 years after termination, for contractual and legal obligations.

Financial & Transaction Records — Invoices, payment records, accounting data. Retained for 6–7 years, in compliance with HMRC and Companies Act requirements.

Employee & Contractor Data — Employment records, payroll, HR data. Retained for the duration of employment plus 6 years after termination, for legal and employment obligations.

Website & Technical Data — IP addresses, analytics data, cookies. Retained for typically 12–26 months depending on tool or provider, for website performance and security.

Support & Communications — Emails, support tickets, enquiries. Retained for up to 3 years from last contact, for customer service and dispute resolution.

3. Data Review & Deletion

We conduct regular data audits to ensure data is accurate, relevant, and not excessive. When data reaches the end of its retention period, it will be securely deleted or anonymised so it can no longer identify individuals.

4. Legal Holds & Exceptions

In certain circumstances, we may retain data beyond standard retention periods where required for legal claims or disputes, regulatory investigations, fraud prevention, or compliance with legal obligations.

5. Data Storage & Security

Data is stored securely using encrypted cloud-based systems, access controls and authentication, and secure backup procedures. Only authorised personnel have access to personal data.

6. Responsibility & Governance

Responsibility for this policy sits with the Company Directors and the Data Protection Lead. All staff and partners handling data are required to follow this policy, undertake appropriate data protection training, and report any data breaches immediately.

7. Policy Review

This Data Retention Policy is reviewed at least annually, or when there are changes to legal or operational requirements. Retention periods are documented in an internal data retention schedule and may be updated where required to reflect legal, regulatory, or operational changes.y.


Legal responsibility for the content on this page sits with Employees Global Ltd.

Data Rights and Requests

At HeroPerks, we respect your rights and are committed to making it easy for you to understand and control how your data is used.

Your Data Rights

Under UK data protection law, you have the right to:

Access your data — request a copy of the personal data we hold about you.

Correct your data — ask us to update or fix any incorrect or incomplete information.

Request deletion — ask us to delete your personal data where there is no valid reason for us to keep it.

Restrict processing — ask us to limit how we use your data in certain circumstances.

Object to processing — object to the use of your data where we rely on legitimate interests (including marketing).

Data portability — request a copy of your data in a structured format to transfer to another provider.

Withdraw consent — where we rely on your consent (e.g. marketing), you can withdraw it at any time.

How to Make a Request

Making a request is simple. You can contact us by: [email protected]

Please include your name, the email address linked to your account, and the type of request you are making. This helps us respond quickly and securely.

What Happens Next

  • We will acknowledge your request as soon as possible
  • We may need to verify your identity to protect your data
  • We aim to respond within one month, in line with legal requirements
  • If your request is complex, we will keep you updated

There is usually no charge for making a request.

When We May Not Be Able to Comply

In some cases, we may not be able to fulfil a request, for example if we are legally required to keep certain data, the request would impact the rights of others, or the request is excessive or unfounded. If this applies, we will explain clearly why.

Complaints

If you’re unhappy with how we’ve handled your request, you have the right to raise a concern with the Information Commissioner’s Office (ICO). You can contact them via https://ico.org.uk.

Our Registration

HeroPerks (Employees Global Ltd) is registered with the Information Commissioner’s Office under registration number ZB574307.

Our Commitment

We are committed to handling all data rights requests fairly, transparently, and in line with UK data protection laws.


Legal responsibility for the content on this page sits with Employees Global Ltd.

Privacy Policy

This Privacy Policy explains how HeroPerks collects, uses, and protects your personal data when you use our website and services. We are committed to handling your data transparently and in accordance with UK data protection laws, including the UK GDPR and the Data Protection Act 2018.

1. Who We Are

HeroPerks is a platform that connects employees within Partner Organisations with exclusive offers, services, and trusted local businesses. For the purposes of data protection law, we act as a Data Controller when determining how and why your personal data is used.

2. What Information We Collect

Personal Information — Name, email address, and contact details

Account Information — Login details, preferences, and usage activity

Business / Partner Information — Business contact details and service information (where applicable)

Technical Data — IP address, browser type, device information, and cookies

Communication Data — Messages, enquiries, and support requests

We do not intentionally collect sensitive (special category) data unless required and lawful.

3. How We Collect Your Data

We collect data when you register or create an account, subscribe to emails or updates, contact us directly, use our website (via cookies and analytics tools), or interact with partner listings or services.

4. How We Use Your Data

We use your data to provide and manage your account, deliver relevant offers and services, communicate with you, improve our platform and user experience, manage partnerships and listings, and comply with legal obligations.

5. Lawful Basis for Processing

Consent — for marketing communications

Contract — to provide our services

Legal obligation — to meet regulatory requirements

Legitimate interests — to improve our platform and prevent misuse

6. How We Share Your Data

We may share your data with trusted third parties where necessary, including technology and hosting providers, email and communication platforms, payment processors, professional advisers, and regulatory authorities (where required). All third parties are required to process your data securely and only for agreed purposes. We do not sell your personal data.

7. Data Security

We take appropriate steps to protect your data, including secure systems and infrastructure, access controls and permissions, encryption where appropriate, and regular monitoring and updates. Only authorised individuals have access to your data.

8. International Transfers

Where data is transferred outside the UK, we ensure appropriate safeguards are in place, such as UK adequacy decisions, standard contractual clauses, or approved legal mechanisms.

9. How Long We Keep Your Data

We only retain your data for as long as necessary. For more information, please see our Data Retention Policy.

10. Your Rights

You have the right to access your personal data, correct inaccurate information, request deletion (where applicable), restrict or object to processing, request transfer of your data, and withdraw consent at any time. To exercise your rights, please see Data Rights & Requests.

11. Cookies

We use cookies and similar technologies to improve your experience and understand how our website is used. For more details, please see our Cookie Policy.

12. Data Breaches

We have procedures in place to detect and respond to data breaches. Where required, we will notify the Information Commissioner’s Office (ICO) and affected individuals.

13. Changes to This Policy

We may update this Privacy Policy from time to time to reflect changes in our services or legal obligations. This Privacy Policy should be read alongside our Data Handling Policy, Data Retention Policy, and Cookie Policy.

14. Contact Us

If you have any questions about this Privacy Policy or your data, please contact: [email protected]


Legal responsibility for the content on this page sits with Employees Global Ltd.

Terms Of Use

These Terms of Use govern your access to and use of the HeroPerks website and services. By using our platform, you agree to comply with these terms. If you do not agree with these Terms of Use, you should not use our website or services.

1. About HeroPerks

HeroPerks is a platform that connects employees within Partner Organisations with exclusive offers, services, and trusted local businesses.

2. Eligibility

To use our platform, you must be at least 18 years old, provide accurate and truthful information, and use the platform for lawful purposes only. We reserve the right to restrict access where these conditions are not met.

3. Use of the Platform

You agree to use the platform responsibly and in good faith, not to misuse or attempt to disrupt the website, not to use the platform for fraudulent or unlawful activity, and not to attempt to gain unauthorised access to systems or data.

4. Accounts

If you create an account, you are responsible for maintaining the confidentiality of your login details, you must notify us if you suspect unauthorised access, and we may suspend or terminate accounts where misuse is identified.

5. Offers and Partner Services

HeroPerks provides access to offers and services from third-party businesses. All offers are provided by independent partners; terms, availability, and pricing are set by those partners; and we do not guarantee the quality, availability, or outcomes of third-party services. Any agreement you enter into with a partner is directly between you and that business.

6. Intellectual Property

All content on the HeroPerks platform, including text, branding, and design, is owned by or licensed to HeroPerks. You may not copy, reproduce, or distribute content without permission, or use our branding without prior approval.

7. Privacy and Data Protection

Your use of the platform is also governed by our Privacy Policy, Data Handling Policy, Data Retention Policy, and Cookie Policy. These explain how your personal data is collected and used.

8. Limitation of Liability

To the extent permitted by law, HeroPerks is not liable for any indirect or consequential loss, we are not responsible for third-party services or partner offers, and we do not guarantee uninterrupted or error-free access to the platform. Nothing in these terms limits liability where it cannot legally be excluded.

9. Changes to the Service

We may update or modify the platform, add or remove features, and change or withdraw offers. We will aim to minimise disruption where possible.

10. Suspension or Termination

We reserve the right to suspend or terminate access where these Terms of Use are breached, there is suspected misuse or unlawful activity, or it is necessary to protect the platform or users.

11. Changes to These Terms

We may update these Terms of Use from time to time. Continued use of the platform means you accept any updated terms.

12. Governing Law

These Terms of Use are governed by the laws of England and Wales. If you are a business partner using the platform, additional terms may apply under a separate agreement.

13. Contact Us

If you have any questions about these Terms of Use, please contact: [email protected]


Legal responsibility for the content on this page sits with Employees Global Ltd.

Cookie Policy

This Cookie Policy explains how cookies and similar technologies are used across the HeroPerks platform, including heroperks.co.uk and its subdomains such as members.heroperks.co.uk.

What are cookies?

Cookies are small text files stored on your device when you visit a website. They help the platform function correctly, remember your preferences, and provide information about how the platform is used.

Cookies may be either session cookies, which are deleted when you close your browser, or persistent cookies, which remain on your device for a set period or until deleted.

How cookies are used

Cookies are used to:

  • Enable core platform functions such as security, navigation, and access to secure areas
  • Remember your preferences and settings
  • Understand how the platform is used so it can be improved

Managing your cookie preferences

Cookie preferences on the platform are managed through CookieYes. When you first visit, you can choose which categories of non-essential cookies to accept or reject. You can change your preferences at any time using the cookie preference centre, accessible via the footer links.

Essential cookies cannot be disabled as they are necessary for the platform to function. You can also control cookies through your browser settings, though disabling some cookies may affect how the platform works.

Cookies used on the platform

The table below lists the cookies currently in use, including their purpose, provider, and duration. It is maintained automatically and reflects the cookies active on the platform.

[cookie_audit]

Changes to this policy

This Cookie Policy may be updated from time to time to reflect changes in technology, law, or the operation of the platform. The date at the top of this page indicates when it was last updated.

For more information on how long data is retained, see the Data Retention Policy.


Legal responsibility for the content on this page sits with Employees Global Ltd.

Data Processing Agreement

Relating to the processing of personal data


This Data Processing Agreement (the “Agreement”) is made between:

(1) Employees Global Ltd, trading as HeroPerks, a company registered in England and Wales (Company No. 15032559), whose registered office is at Colony Fabrica, Great Ancoats Street, Manchester, England, M4 7DB (the “Controller”); and

(2) 3manfactory Ltd, a company registered in England and Wales (Company No. 07642302), whose registered office is at Old Docks House, 90 Watery Lane, Preston, Lancashire, PR2 1AU (the “Processor”),

each a “Party” and together the “Parties”.

Background

A. The Controller operates a Licensed Instance of the EAPP Platform (the “Platform”) under the brand HeroPerks.

B. The Processor provides hosting, maintenance, and technical operation of the Platform to the Controller under a separate Platform Licence & Revenue Share Agreement between the Parties dated 11 February 2026 (the “Licence Agreement”). The Processor is the Licensor and the Controller is the Licensee under the Licence Agreement.

C. In the course of providing those services, the Processor processes personal data on behalf of the Controller. This Agreement sets out the terms on which the Processor processes that personal data and is entered into to satisfy the requirements of Article 28 of the UK GDPR.

D. This Agreement supplements and forms part of the Licence Agreement. In the event of conflict between this Agreement and the Licence Agreement in relation to the processing of personal data, this Agreement prevails.

1. Definitions and Interpretation

1.1 In this Agreement, the following definitions apply:

“Data Protection Legislation” means all applicable laws relating to the processing of personal data and privacy, including the UK GDPR, the Data Protection Act 2018, and the Privacy and Electronic Communications Regulations 2003, in each case as amended or replaced from time to time.

“UK GDPR” means the retained EU law version of the General Data Protection Regulation (Regulation (EU) 2016/679) as it forms part of the law of England and Wales by virtue of the European Union (Withdrawal) Act 2018.

“Personal Data” means personal data (as defined in the UK GDPR) processed by the Processor on behalf of the Controller under this Agreement, as further described in Annex 1.

“Processing” has the meaning given in the UK GDPR, and “Process” and “Processed” are construed accordingly.

“Data Subject” means an identified or identifiable natural person to whom the Personal Data relates.

“Personal Data Breach” means a breach of security leading to the accidental or unlawful destruction, loss, alteration, unauthorised disclosure of, or access to, Personal Data.

“Sub-Processor” means any third party engaged by the Processor to process Personal Data in connection with the provision of services under the Licence Agreement.

“Sub-Processor Charges” means the Revenue Share and other charges payable by the Controller to the Processor under the Licence Agreement.

1.2 Terms not otherwise defined in this Agreement have the meaning given in the Licence Agreement.

1.3 References to any statute or statutory provision include that statute or provision as amended, replaced, or re-enacted from time to time.

2. Roles of the Parties

2.1 The Parties acknowledge that, for the purposes of the Data Protection Legislation, the Controller is the data controller and the Processor is the data processor in respect of the Personal Data.

2.2 The Controller is responsible for determining the purposes and means of the Processing of Personal Data, and for ensuring that it has a valid lawful basis for the Processing and that all necessary notices and consents are in place to enable the lawful transfer of Personal Data to the Processor for the duration and purposes of this Agreement.

2.3 The Processor processes Personal Data only on behalf of the Controller and in accordance with this Agreement.

3. Processor Obligations

The Processor shall:

3.1 process the Personal Data only on documented instructions from the Controller, including with regard to transfers of Personal Data to a third country, unless required to do so by law to which the Processor is subject; in such a case, the Processor shall inform the Controller of that legal requirement before Processing, unless that law prohibits such information on important grounds of public interest;

3.2 ensure that persons authorised to process the Personal Data have committed themselves to confidentiality or are under an appropriate statutory obligation of confidentiality;

3.3 implement and maintain appropriate technical and organisational measures to ensure a level of security appropriate to the risk, in accordance with Article 32 of the UK GDPR, as further described in Annex 2;

3.4 respect the conditions set out in clause 4 of this Agreement for engaging Sub-Processors;

3.5 taking into account the nature of the Processing, assist the Controller by appropriate technical and organisational measures, insofar as this is possible, in fulfilling the Controller’s obligation to respond to requests for exercising Data Subject rights under the Data Protection Legislation;

3.6 assist the Controller in ensuring compliance with its obligations relating to security of Processing, notification of Personal Data Breaches, data protection impact assessments, and prior consultation with the Information Commissioner’s Office, taking into account the nature of Processing and the information available to the Processor;

3.7 at the choice of the Controller, delete or return all Personal Data to the Controller after the end of the provision of services relating to Processing, and delete existing copies unless the law requires storage of the Personal Data; and

3.8 make available to the Controller all information necessary to demonstrate compliance with the obligations set out in Article 28 of the UK GDPR and allow for and contribute to audits, including inspections, in accordance with clause 7.

3.9 The Processor shall immediately inform the Controller if, in its opinion, an instruction given by the Controller infringes the Data Protection Legislation.

3.10 The assistance and cooperation described in clauses 3.5, 3.6, and 3.8 shall be provided by the Processor, and the Controller shall reimburse the Processor’s reasonable costs incurred in providing such assistance, save where such assistance is required as a direct result of the Processor’s breach of this Agreement.

4. Sub-Processors

4.1 The Controller grants the Processor general written authorisation to engage the Sub-Processors listed in Annex 3 for the Processing of Personal Data.

4.2 The Processor may engage additional or replacement Sub-Processors provided that it gives the Controller prior written notice of the intended change, thereby giving the Controller the opportunity to object to such changes. Notice may be given by email or by updating the Sub-Processor list published on the HeroPerks Trust Centre and notifying the Controller of the update.

4.3 If the Controller objects to a new or replacement Sub-Processor on reasonable data protection grounds within fourteen (14) days of notice, the Parties shall work together in good faith to resolve the objection. If no resolution is reached, the Processor may either decline to appoint the Sub-Processor or, where this is not commercially practicable, either Party may terminate the affected services on reasonable notice.

4.4 Where the Processor engages a Sub-Processor, it shall do so by way of a written contract imposing data protection obligations substantially equivalent to those set out in this Agreement. The Processor remains liable to the Controller for the performance of the Sub-Processor’s obligations in accordance with the liability provisions in clause 9.

5. Security of Processing

5.1 The Processor shall implement and maintain the technical and organisational measures described in Annex 2, taking into account the state of the art, the costs of implementation, and the nature, scope, context, and purposes of Processing, as well as the risk to the rights and freedoms of Data Subjects.

5.2 The current technical and organisational measures applied to the Platform are also published and maintained on the HeroPerks Trust Centre. The measures set out in Annex 2 represent the agreed baseline as at the date of this Agreement. The Processor may update its measures from time to time provided that any update does not materially reduce the overall level of security.

6. Personal Data Breach

6.1 The Processor shall notify the Controller without undue delay, and in any event within forty-eight (48) hours, after becoming aware of a Personal Data Breach affecting the Personal Data.

6.2 Such notification shall, to the extent reasonably available to the Processor, describe the nature of the Personal Data Breach, the categories and approximate number of Data Subjects and records concerned, the likely consequences, and the measures taken or proposed to address the breach.

6.3 The Processor shall cooperate with the Controller and take such reasonable steps as are directed by the Controller to assist in the investigation, mitigation, and remediation of the Personal Data Breach.

6.4 The Controller is responsible for any notification of a Personal Data Breach to the Information Commissioner’s Office and to affected Data Subjects, as required under the Data Protection Legislation.

7. Audit and Inspection

7.1 The Processor shall make available to the Controller all information reasonably necessary to demonstrate compliance with this Agreement and shall, on reasonable prior written notice, allow for and contribute to audits conducted by the Controller or an auditor mandated by the Controller.

7.2 Audits shall be limited to once per calendar year, save where an audit is required following a Personal Data Breach or by a supervisory authority. Audits shall be conducted during normal business hours, with a minimum of thirty (30) days’ prior written notice, in a manner that minimises disruption to the Processor’s business, and subject to appropriate confidentiality undertakings.

7.3 The Controller shall bear its own costs and the Processor’s reasonable costs in relation to any audit, save where the audit reveals a material breach of this Agreement by the Processor, in which case the Processor shall bear its own costs.

8. International Transfers

8.1 The Processor shall not transfer Personal Data to a country outside the United Kingdom without the prior written consent of the Controller, except as already provided for through the Sub-Processors listed in Annex 3.

8.2 Where any transfer of Personal Data outside the United Kingdom is authorised, the Processor shall ensure that an appropriate transfer mechanism recognised under the Data Protection Legislation is in place.

9. Liability and Indemnity

9.1 Subject to clause 9.3, the total aggregate liability of the Processor arising out of or in connection with this Agreement, whether in contract, tort (including negligence), breach of statutory duty, or otherwise, shall not exceed a sum equal to the total Sub-Processor Charges paid by the Controller to the Processor in the twelve (12) month period immediately preceding the event giving rise to the liability.

9.2 The Controller shall indemnify and keep indemnified the Processor against all losses, claims, damages, liabilities, fines, costs, and expenses (including reasonable legal fees) arising out of or in connection with: (a) any breach by the Controller of its obligations under this Agreement or the Data Protection Legislation; (b) any Processing carried out by the Processor in accordance with the Controller’s documented instructions; and (c) any claim that the Controller did not have a valid lawful basis for the Processing or failed to provide required notices to or obtain required consents from Data Subjects.

9.3 Nothing in this Agreement shall limit or exclude either Party’s liability for: (a) death or personal injury caused by its negligence; (b) fraud or fraudulent misrepresentation; (c) any matter for which it would be unlawful to limit or exclude liability; (d) the Controller’s indemnity obligations under clause 9.2; or (e) either Party’s breach of its confidentiality obligations.

9.4 The limitation of liability in clause 9.1 is without prejudice to any limitation or exclusion of liability set out in the Licence Agreement, and the two shall be read together; where both apply to the same loss, the lower applicable cap shall prevail and the Controller shall not recover more than once in respect of the same loss.

10. Term and Termination

10.1 This Agreement takes effect on the Effective Date of the Licence Agreement and shall remain in force for the same term as the Licence Agreement, including any renewal periods, terminating automatically on termination or expiry of the Licence Agreement.

10.2 On termination or expiry of this Agreement, the Processor shall, at the choice of the Controller, delete or return all Personal Data in accordance with clause 3.7, save that the Processor may retain Personal Data to the extent required by applicable law and for the period of any backup retention cycle, after which it shall be securely deleted.

11. General

11.1 This Agreement is governed by the laws of England and Wales, and the courts of England and Wales have exclusive jurisdiction to settle any dispute arising out of or in connection with it.

11.2 No variation of this Agreement is effective unless made in writing and signed by or on behalf of each Party.

11.3 If any provision of this Agreement is found to be invalid or unenforceable, the remaining provisions shall continue in full force and effect.

11.4 This Agreement, together with the Licence Agreement, constitutes the entire agreement between the Parties in relation to the Processing of Personal Data and supersedes any prior arrangement in respect of the same subject matter.


This Agreement was executed by both parties and took effect on 11 February 2026.


Annex 1 — Details of Processing

Subject matter: Processing of Personal Data necessary for the hosting, maintenance, and technical operation of the HeroPerks Platform.

Duration: For the term of the Licence Agreement, including any renewal periods, and any subsequent retention period permitted under clause 10.2.

Nature and purpose: Storage, hosting, transmission, and processing of Personal Data to enable user registration, account management, delivery of platform functionality, and platform communications.

Type of Personal Data: Name; email address; platform activity data; profile data. No special category data is processed.

Categories of Data Subject: Members; Local Suppliers; Recommended Professionals.


Annex 2 — Technical and Organisational Measures

The technical and organisational measures agreed under this Agreement are those maintained on the platform and published across the Security and Platform sections of this Trust Centre. See Platform Security Principles, Platform Access Controls, and Platform Infrastructure & Hosting.


Annex 3 — Authorised Sub-Processors

The authorised sub-processors under this Agreement are listed on the Platform Sub-Processors page, which is maintained as the current record.


Legal responsibility for the content on this page sits with Employees Global Ltd.